IP-hardening a Python product: compiled binaries, no source in production
Shipping a Python product without shipping your Python source: what compiling to binaries actually protects, and what it doesn't.
By Agent Software
The exposure nobody thinks about until it matters
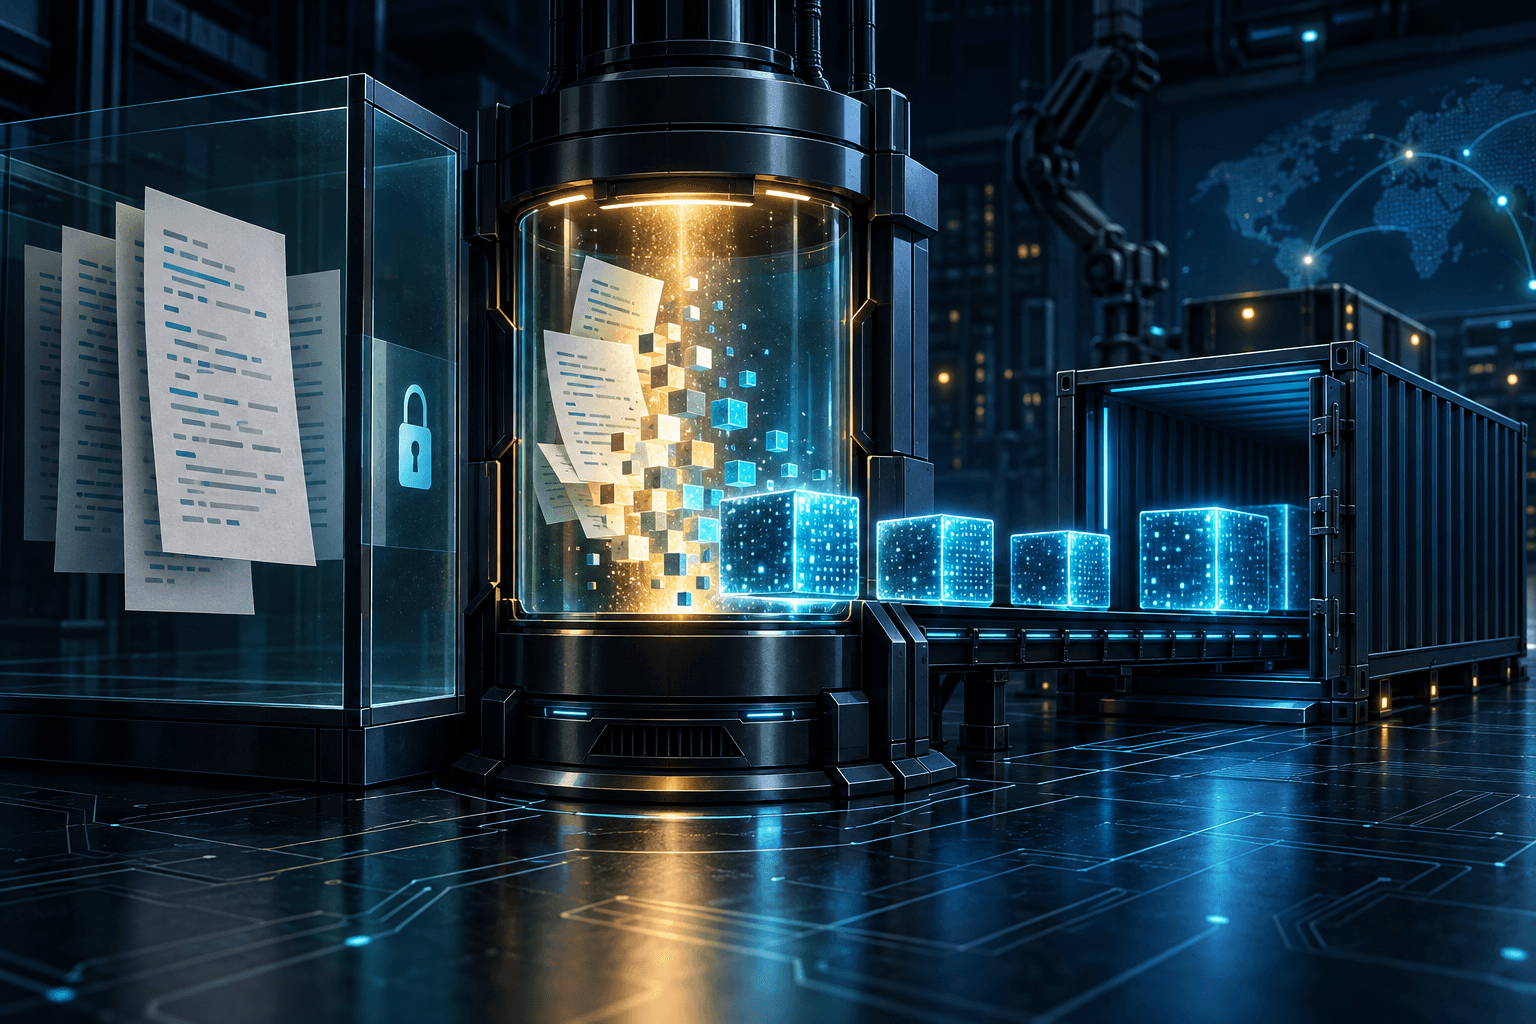
Python's readability is one of its biggest advantages during development — and one of its biggest liabilities in production. A .py file shipped inside a container image is, functionally, documentation for anyone who gets shell access to that container: every function, every constant, every scoring formula, laid out in plain text.
For most internal tooling that's a non-issue. For a product whose competitive value is partly in the specific implementation — how a ranking formula weighs its inputs, how a caching threshold was tuned — it's a real exposure.
What compiling to binaries changes
Agent Brain's production images don't contain .py source at all. The Python codebase is compiled ahead of time into native binaries, and only those binaries ship in the deployed artifact. Someone with access to a running container can inspect the compiled code, but they don't get a plain-text readout of the implementation the way they would with interpreted source sitting on disk.
What this doesn't replace
This is worth being precise about: compiling source away is not a substitute for actual access controls, authentication, or network security. If someone has legitimate reasons to be inside the container in the first place, real security still depends on limiting what they can reach and do there. Removing readable source closes one specific door — casual inspection of the implementation — not every door.
Why this matters more for a self-hosted product
Because Agent Brain runs self-hosted, on infrastructure the customer controls, the product has less control over the runtime environment than a SaaS vendor running everything on their own servers. Compiling the source away is a way to protect the implementation even when the binary itself is running somewhere outside the company's own infrastructure.
The honest tradeoff
Compiled binaries are harder to debug in the field and add a build step that plain interpreted Python doesn't need. That's a real cost, taken on deliberately because the alternative — shipping readable source in every self-hosted deployment — was judged to be the bigger risk.