Why an in-app companion should be loopback-only and local-first
The security reasoning behind restricting Agent Assistant's companion service to loopback-only connections instead of a network-accessible service.
By Agent Software
The attack surface problem of an embedded AI companion
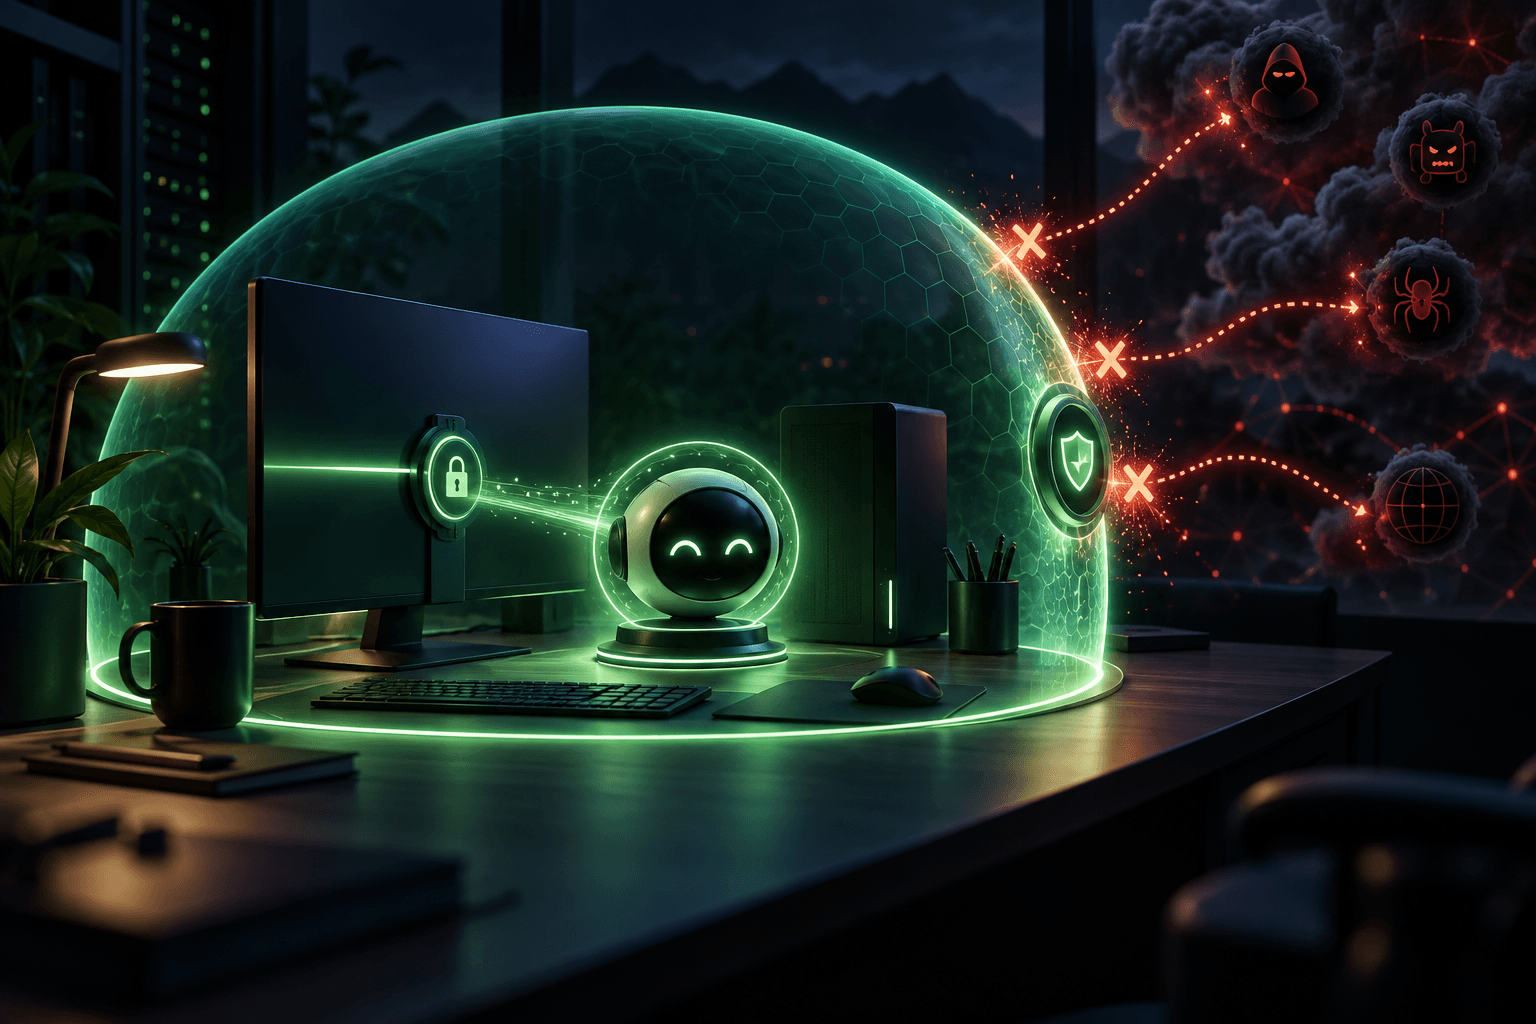
An AI companion that lives inside other applications — able to see UI state, suggest actions, and execute commands on your behalf — is powerful precisely because it has more access than a typical background service. That power is also exactly why it needs a tighter trust boundary than most services get by default.
Loopback-only as the starting assumption
Familiar's service listens only on 127.0.0.1, the local loopback interface. Nothing outside the machine it's running on can reach it — not by misconfiguration, not by an open port left exposed, because there's no network-facing listener to expose in the first place. This is a design decision made at the start, not a firewall rule added after the fact.
Host authentication as the second gate
Loopback-only stops remote access, but it doesn't by itself stop a different local process from pretending to be a legitimate host application. That's where host authentication comes in: connecting apps have to present cryptographic proof (HMAC-based) that they're who they claim to be before Familiar will talk to them at all. Two gates, not one.
Why this has to be designed in, not added later
A service built to accept connections from anywhere and later restricted to loopback-only carries the assumptions of its original design — network protocol choices, authentication that was optional rather than mandatory, code paths that were never meant to be the only path. Starting from "nothing outside this machine can reach this, ever" avoids all of that, at the cost of some flexibility Familiar simply doesn't need.
Foreground-only as a related boundary
The same philosophy extends to which app on your machine Familiar will actually act on behalf of: only the foreground, currently-focused host application, never a background one. That closes off a class of privilege-escalation attempts where a background app tries to trigger actions meant for whatever you're actively looking at.
An honest status note
Agent Assistant (Familiar) is an internal project in development, currently used inside the suite's own products rather than offered as a standalone, publicly available service. The security model described here reflects the actual current design, not a future promise.